ISO/IEC 20000-1
ISO 20000-1 Certification – Run IT Services on Process, Not Heroics
Table of Contents
Think about the last time a client system went down on a Friday evening. Who got the call? How long before someone owned the ticket? Was the fix written down anywhere, or did it live in one engineer’s head? If you’re looking for “whoever picked up” as an answer to the first question, “too long” to the second, and “his head” to the third, then ISO 20000-1 certification is for you.
IT Service Management System (SMS) is a global standard for IT Service Management – ISO/IEC 20000-1. It outlines the planning, provision, support and enhancement of information technology services, to ensure the delivery of consistent services to customers. ISPL provides your people with training and audits for ISO 20000-1 certification. We don’t write your procedures for you, and the why is described below.
The scope of ISO 20000-1 Certification.
ISO 20000-1 certification fits any organization that delivers IT services. That includes managed service providers, software and SaaS companies, data centres, BPOs with a service desk, and internal IT departments serving the rest of a large company.
The standard asks for a working service management system, which in practice means a few things you may only half do today:
- Service catalogues and agreed service levels, so everyone knows what is promised
- Incident handling with clear ownership and response targets
- Problem management, which hunts the root cause instead of fixing the same fault weekly
- Change and release control, so an update does not break production
- Asset and configuration records that match what is really installed
- Capacity, availability and continuity planning
- Supplier management, since many IT services lean on third parties
If you are already familiar with ITIL, much of this will be familiar. On top of that ISO 20000-1 adds an external audit, making good habits manifest.
The reasons why businesses opt for ISO 20000-1 Certification.
The first reason is trust. Ineffective service delivery is a frequent requirement from enterprise buyers and government departments of their outsourcing partners. A certificate responds that prior to the first meeting.
The second is less repeated failures. Patterns emerge after incidents, changes and problems are documented and analysed. The crash every quarter is no longer a surprise if the server does crash. The third is tenders. ISO 20000-1 is included on quite a few bids for IT outsourcing and managed services, and it is sometimes included in the scoring for the bid.
The third is tenders. Many IT outsourcing and managed services bids list ISO 20000-1 certification as a requirement or give extra marks for it.
Last, but not least, staff stability. If there are procedures in place, a new engineer can join the queue in days, not weeks.
Who Should Consider ISO 20000-1 Certification
ISO 20000-1 certification suits you if:
- You sell managed IT or support services to external clients
- Customers or tenders ask for proof of service management maturity
- Your service desk handles a growing ticket volume and quality is uneven
- You run internal IT for a large group and want measurable service levels
A two-person consultancy with a handful of clients may not need ISO 20000-1 certification yet. A provider with a service desk, SLAs and multiple customers usually does.
How the ISO 20000-1 Certification Process Works
Our role in ISO 20000-1 certification has two parts: training and audit. This is how it runs.
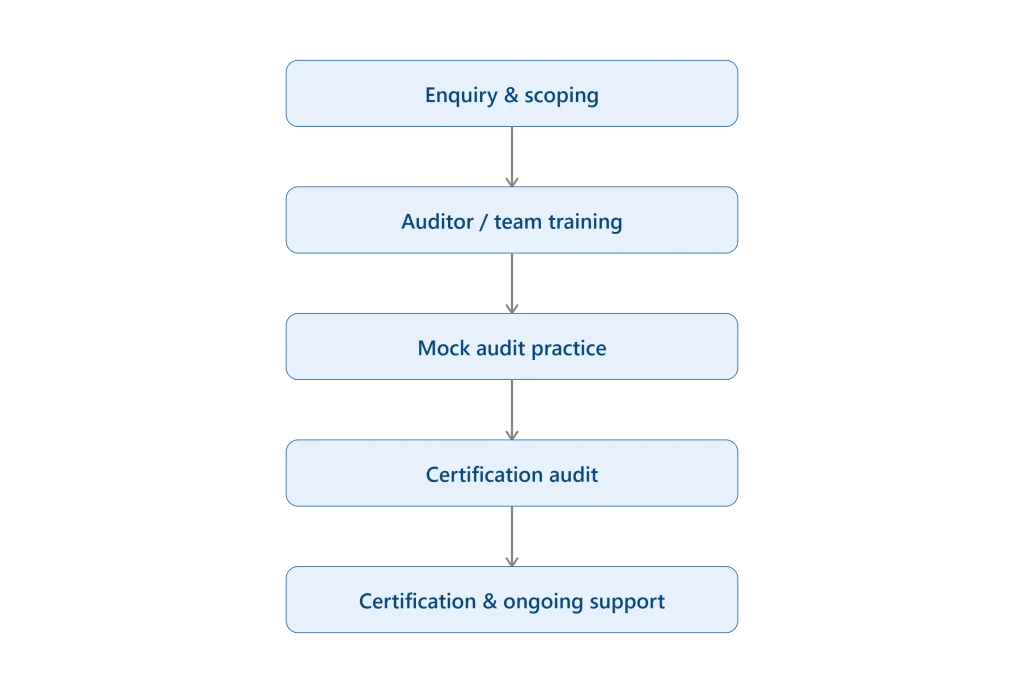
- Enquiry and scoping. We learn which services, locations and teams are in scope, and what outcome you want.
- Auditor and team training. Your staff learn the ISO 20000-1 requirements and how a service management audit is carried out. Examples come from real service desks, not only clause text.
- Mock audit. A rehearsal with the kind of questions an auditor will ask, early enough to fix weak spots.
- Certification audit. Our auditors assess your system against the standard, independently, with evidence checked on site or remotely.
- Certification and ongoing support. When findings are closed, the certificate is issued. We remain available for annual surveillance audits.
Common Slip-Ups Before ISO 20000-1 Certification
Teams tend to trip over the same things.
- Tickets closed without a record of the fix. An auditor will sample closed incidents and ask what was done.
- Changes made outside the change process. Emergency changes are allowed, but they still need a record and a review afterwards.
- SLAs nobody measures. A target on paper with no report behind it counts for nothing.
- Stale asset lists. If the configuration records do not match the live environment, expect a finding.
- Management review skipped. Senior people need to look at service performance on a schedule, and the minutes should show it.
Training ahead of the audit clears most of these, which is why we place it before the certification audit.
What You Gain From ISO 20000-1 Certification
The headline gain of ISO 20000-1 certification is steadier service. Fewer repeat incidents, faster restoration and cleaner handovers all come from the same discipline. You also get a stronger position in outsourcing tenders, better reporting for your own management, and a clearer picture of where engineering time actually goes.
Why ISPL
ISPL is an EGAC-accredited certification body with years of ISO training and audit work behind it. For ISO 20000-1 certification we offer:
- Training for auditors and service teams on the standard
- Mock audit sessions before the real one
- Independent certification audits
- Support through surveillance and renewal audits
Getting Started
The time required to receive ISO 20000-1 certification varies depending on your existing processes. With a provider that includes a ticketing system, certain defined SLAs and monthly reporting, they can go fast. Normally, a team that works mainly with chat and memory takes time to create records first. The ISO 20000-1 certificate remains valid for three years, with a surveillance audit yearly between the initial and recertification audit. To find out what it would look like to be ISO 20000-1 certified by you, please submit your services, staffing size and number of locations.We will outline the training and audit plan.
Contact Us
Phone: +91-9990477631 Email: info@isplcmmi.com
Get In Touch
Fill out the form and our team will get back to you shortly.
Our Services
ISO 9001 → ISO 14001 → ISO 45001 → ISO 22000 → ISO/IEC 20000-1 → ISO/IEC 27001 → ISO 22301 → ISO/IEC 42001 → CMMI Certification → VAPT → SOC Reporting → ISO 50001 →Latest Blogs
 ISO 27001 Certification Cost in India for IT Companies: Complete Guide
October 15, 2026
 ISO Certification agency in India for 2026
October 12, 2026
 Documents Required for ISO 9001 Certification: Complete Checklist
October 7, 2026
 VAPT Testing Cost in India: Complete Guide for Businesses in 2026
October 5, 2026
 CMMI Level 3 Certification Cost in India: Complete 2026 Guide
September 30, 2026