ISO 27001 Certification
About ISO 27001 Certification
ISO 27001 Certification – Protect What Actually Matters
A security policy saved on a shared drive doesn’t protect anyone’s data, and neither does a slide deck from a one-time training session. ISO 27001 certification exists for organizations that want information security to be more than a document — it gives you a structured Information Security Management System (ISMS) built to manage real risks to sensitive data, not just describe them in a PDF nobody opens.
At ISPL, we help organizations get their teams trained and their information security systems audited against ISO 27001, so the certification reflects practices that genuinely protect data, rather than paperwork assembled the week before an auditor arrives.
What ISO 27001 Certification Actually Covers
ISO 27001 certification is built on an international standard for managing information security, and it fits any organization that handles sensitive data — customer records, financial information, or internal business data. None of this is about avoiding breaches on paper. It’s about genuinely reducing the risk of information getting compromised, through controls people actually follow.
Organizations pursuing ISO 27001 certification typically end up working through a handful of core areas: identifying risks to sensitive data and systems, protecting information from unauthorized access, meeting legal and regulatory data protection requirements, setting up clear access controls and policies, and building real employee awareness around data security instead of a once-a-year training video.
Why Pursue ISO 27001 Certification
There are a few concrete reasons businesses go after ISO 27001 certification.
Reduced Data Breaches — catching security gaps before they get exploited beats dealing with the fallout afterward.
Client Trust — clients feel noticeably safer sharing data with a business that’s gone through independent certification, rather than one that simply says it takes security seriously.
Regulatory Compliance — staying ahead of data protection laws avoids scrambling to catch up after a regulator flags something.
Competitive Edge — many contracts now list ISO 27001 certification as a baseline requirement before a vendor is even considered.
Who Should Consider ISO 27001 Certification
ISO 27001 certification tends to suit organizations that handle sensitive customer or financial data, need to meet a client’s data security requirements before signing a contract, want to reduce the risk of cyberattacks or data leaks, or are bidding for contracts that require information security certification as a baseline. It’s also worth considering for growing companies, since informal data-handling habits that worked for a five-person team rarely hold up once client data, staff, and systems multiply.
How the ISO 27001 Certification Process Works
We keep our role narrow, focused on two things — training your team and auditing your system. Here’s how the ISO 27001 certification process actually plays out, step by step:
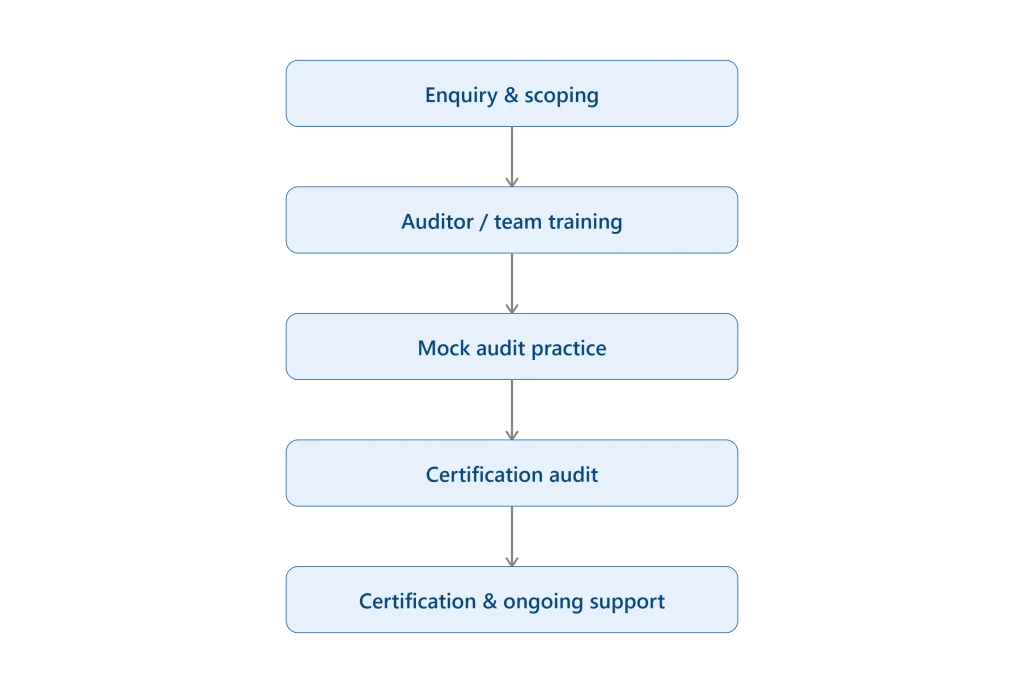
- Enquiry & Scoping — we understand your industry, current data security practices, and what you’re aiming for with certification.
- Auditor / Team Training — your team gets trained on ISO 27001 requirements and how an information security audit is genuinely conducted, not handed a generic checklist.
- Mock Audit Practice — a practice run so your team knows exactly what to expect going into the real audit.
- Certification Audit — our team conducts the formal, independent audit against ISO 27001 requirements.
- Certification & Ongoing Support — once the audit is cleared, certification is issued, and we stay available for surveillance and renewal audits afterward.
We don’t offer consulting, gap analysis, or ISMS design for ISO 27001 certification — that’s a different kind of firm, and it’s not our role. Keeping training and auditing separate from system design means the result stays independent and genuinely credible, since we’re never the ones building what we later audit.
What You Actually Get Out of It
Organizations that complete ISO 27001 certification typically see a reduced risk of data breaches, stronger trust from clients and partners, better regulatory compliance, improved internal data handling practices, and fewer security-related costs over time. There’s also a practical edge when bidding for security-conscious clients who specifically screen vendors on this. Over a few years these gains tend to add up, since fewer incidents also mean less time lost to investigations, notifications, and rebuilding client confidence.
Why ISPL for ISO 27001 Certification
For ISO 27001 certification, we support organizations through training and audits — nothing more, nothing less, and that’s deliberate. It keeps our audits objective and keeps the result meaningful to clients and regulators who actually check rather than glance at a logo.
Our Support Includes:
- Auditor and team training on ISO 27001 requirements
- Mock audit sessions that prepare your team for the real thing
- Formal, independent certification audits
- Ongoing guidance for surveillance and renewal audits after certification
Getting Started with ISO 27001 Certification
Ready to protect your data and build real client trust, not just a compliance checkbox? We can train your team and audit your system through the entire ISO 27001 certification process, start to finish. Whether this is your organization’s first certification or a renewal, things move faster when you start with a clear scope and honest records rather than a scramble before a tender deadline.
Timelines for ISO 27001 certification vary by company size, industry, and how established your current data security practices already are. A smaller SaaS team often moves through this faster than a larger company managing multiple systems, vendors, and client data sets, simply because there’s less ground to cover during training and audit. Businesses already using cloud infrastructure with reasonable access controls in place tend to find the process smoother than those still relying on shared logins and informal data-sharing habits. Once issued, ISO 27001 certification stays valid for three years, with a surveillance audit each year in between to confirm the system is genuinely being followed, not just documented once and forgotten.
Contact Us
Ready to move forward with ISO 27001 certification? Get in touch with our team, and we’ll walk you through exactly what training and audit plan fits your organization and industry.
Contact: +91-9990477631 | info@isplcmmi.com
Get Expert Guidance
Fill out the form and our experts will get in touch with you.
Explore Other ISO Standards
ISO 9001Quality Management System ISO 14001
Environmental Management System ISO 45001
Occupational Health & Safety Management ISO 27001
Information Security Management ISO 22000
Food Safety Management System ISO 50001
Energy Management System ISO 17025
Laboratory Management System ISO 13485
Medical Devices Quality Management IATF 16949
Automotive Quality Management ISO 22301
Business Continuity Management
Need Help Choosing?
Talk to our ISO consultants directly — happy to guide you to the right standard for your business.
☎ +91 - 9990477631 ✉ info@isplcert.com